Keys on your device
We cannot decrypt your end-to-end encrypted mobile messages. Your private keys remain on your device; backup can store wrapped, encrypted key material.

A security suite designed for everyday privacy, personal safety and recovery.
Explore the controls around your conversations, from everyday privacy to recovery.
A secondary PIN provides a personal-safety option if you are being robbed or threatened. Your real account stays protected while you get to safety.
Configure the feature in the app’s security settings and understand how it behaves in your app version. If you are in danger, contact local police. No app can guarantee your physical safety.
PERSONAL SAFETY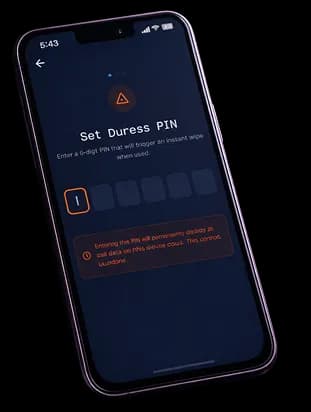
For a lost or stolen phone, designate a trusted contact in advance. That person can help trigger remote removal of your SYNC data from the affected device.
Your SYNC data on that device is erased the next time it connects. A queued request needs a connection to take effect. This is not a factory reset of the whole phone and does not remove copies saved by other people.
REMOTE WIPE · TRUSTED CONTACT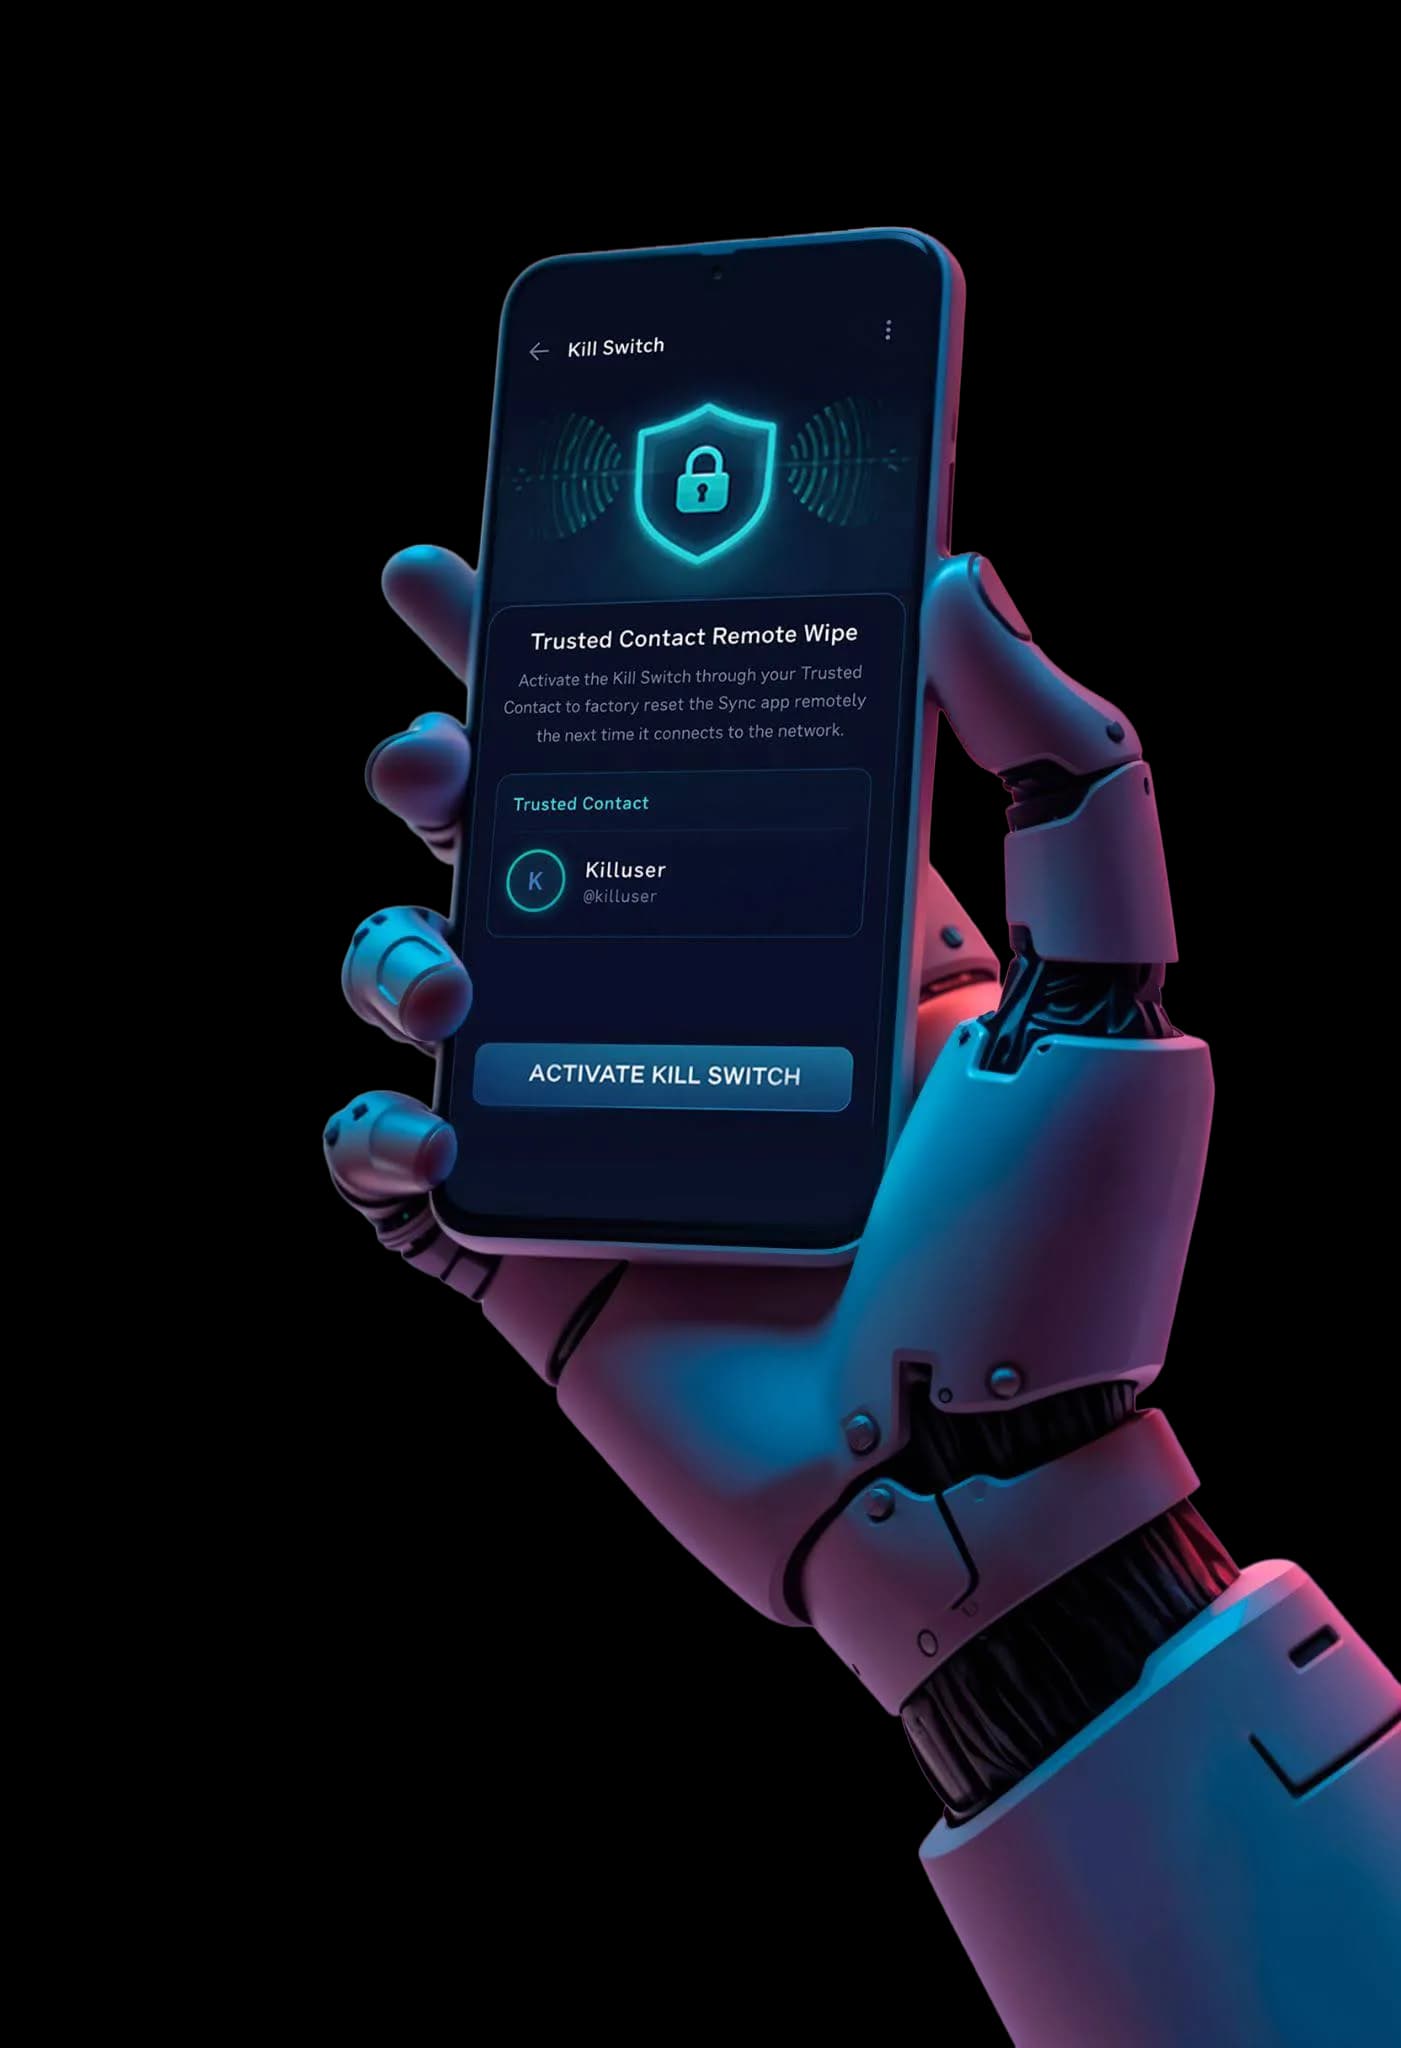
Keep an optional encrypted backup of your chat history so you can restore it on a replacement device. The backup is encrypted before it leaves your device.
Your messages remain available on your phone without an internet connection. Enabling backup adds an encrypted copy for recovery. Keep your recovery information secure and follow the in-app instructions.
OPTIONAL BACKUP · RECOVERY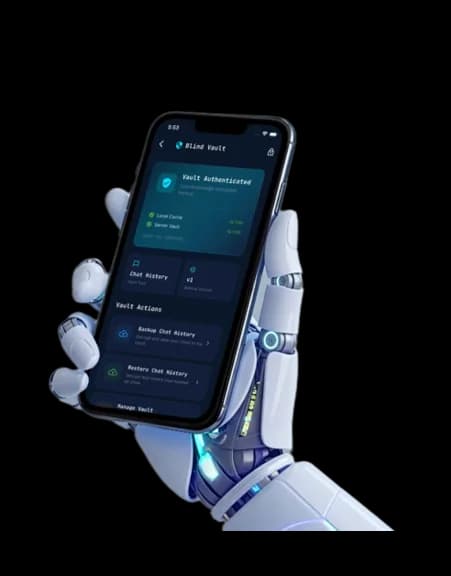
Aegis Shield is designed to protect today’s messages against future quantum attacks.
Its post-quantum approach addresses the risk of encrypted information being collected now and targeted by more powerful computers later.
POST-QUANTUM PROTECTION
Explore shared-secret derivation for messages and a wrapped-master-key flow for Obsidian Core backups. In these examples, the relay receives ciphertext and the information needed to route it, not the plaintext message or backup.
A random master key encrypts the backup. A passphrase-derived key wraps the master key.
Waiting for encrypted dataStored in this browser’s memory onlyCreate a backup to begin.
X25519 combines your private key with the recipient’s public key to derive a shared secret.
No packet received yetRouting information and public keys are not secret.Waiting for an encrypted message.
Compare theoretical key-search sizes. Change the key length and assumed guessing rate to see the estimate respond.
2^256 possible keys. Average search: 2^255 guesses.
Model: half the keyspace ÷ guesses per second. A classical, uniformly random key-search illustration, not observed attacks, measured hardware performance or a guarantee of security. Password guessing, implementation flaws and quantum attacks are different problems.
We cannot decrypt your end-to-end encrypted mobile messages. Your private keys remain on your device; backup can store wrapped, encrypted key material.
Mobile messages and calls use end-to-end encryption. We do not extend this claim to every desktop or web feature without confirmation.
Photos, videos and files are encrypted in transit and at rest. This is distinct from end-to-end encrypted message content.
Essential operational records include device sessions and push tokens. Temporary IP logs may be retained for up to 90 days for security and abuse prevention.
Start with a conversation.